
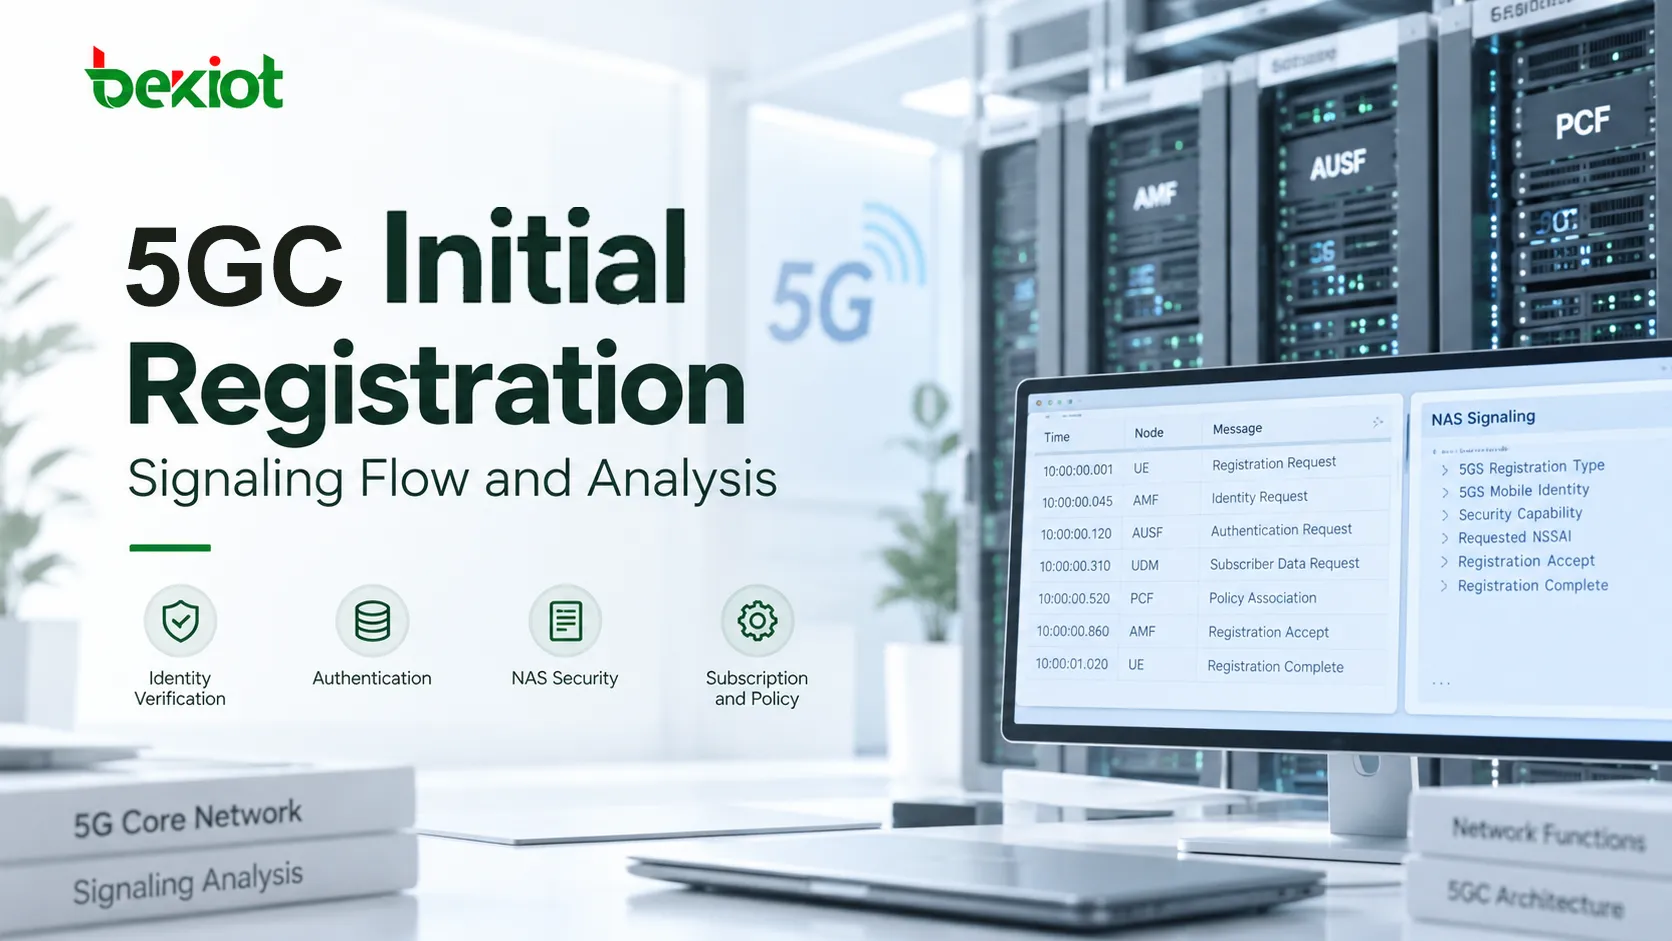
5G Initial Registration establishes the UE’s registration and access-and-mobility context. The AMF resolves who the subscriber is, applies the required security procedures and determines permitted access and slices. Registration success alone does not establish an Internet data path: PDU Session Establishment is a separate procedure.
Separate RRC, NGAP and NAS in the Trace
For an ordinary NR access example, the UE establishes or uses an RRC signaling connection with the gNB. RRC carries the NAS Registration Request over the radio interface. The gNB forwards the NAS-PDU to the AMF in an NGAP Initial UE Message, together with access-location information such as TAI and NR-CGI. NAS runs logically between UE and AMF; NGAP runs between gNB and AMF.
The NAS 5GS registration type identifies initial registration, mobility registration updating, periodic registration updating or emergency registration in the ordinary cases discussed here. The mandatory mobile identity and conditionally present information serve different purposes. A usable 5G-GUTI can refer to earlier context; otherwise SUCI is commonly used under the identity-selection rules. Requested NSSAI and UE Security Capability are included according to the applicable NAS conditions, rather than being an invariant field list for every request.
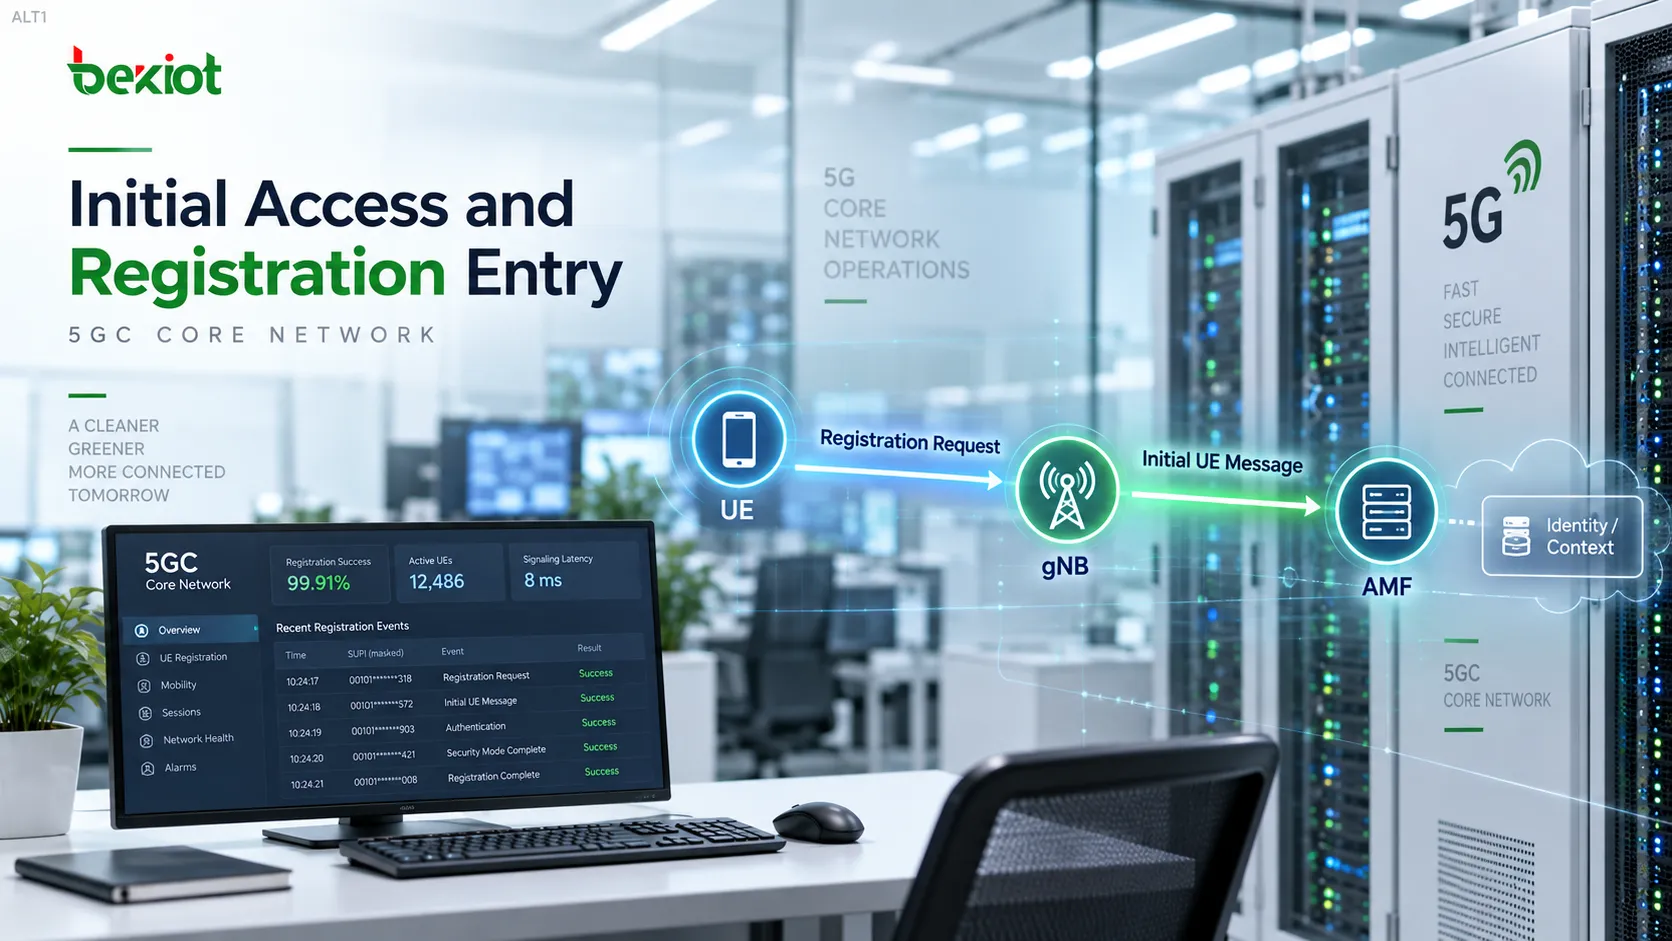
Resolve Identity and Reuse Previous Context When Available
“Initial” describes the registration type, not necessarily a subscriber’s first-ever use of 5G. For example, a UE powered off in Guangzhou and restarted in Beijing may still hold a 5G-GUTI. Its GUAMI can help identify the previous AMF. When applicable, the new AMF invokes Namf_Communication_UEContextTransfer to retrieve identity and mobility context, including available security information.
Old-AMF interaction is conditional. If the AMF needs an identity that it cannot otherwise obtain, a NAS Identity Request and Identity Response can supply the requested identity, such as SUCI. Neither a context transfer nor an Identity Request must appear in every successful trace. Check the identity and context already available before declaring a missing message to be a fault.
Authentication and NAS Security Solve Different Problems
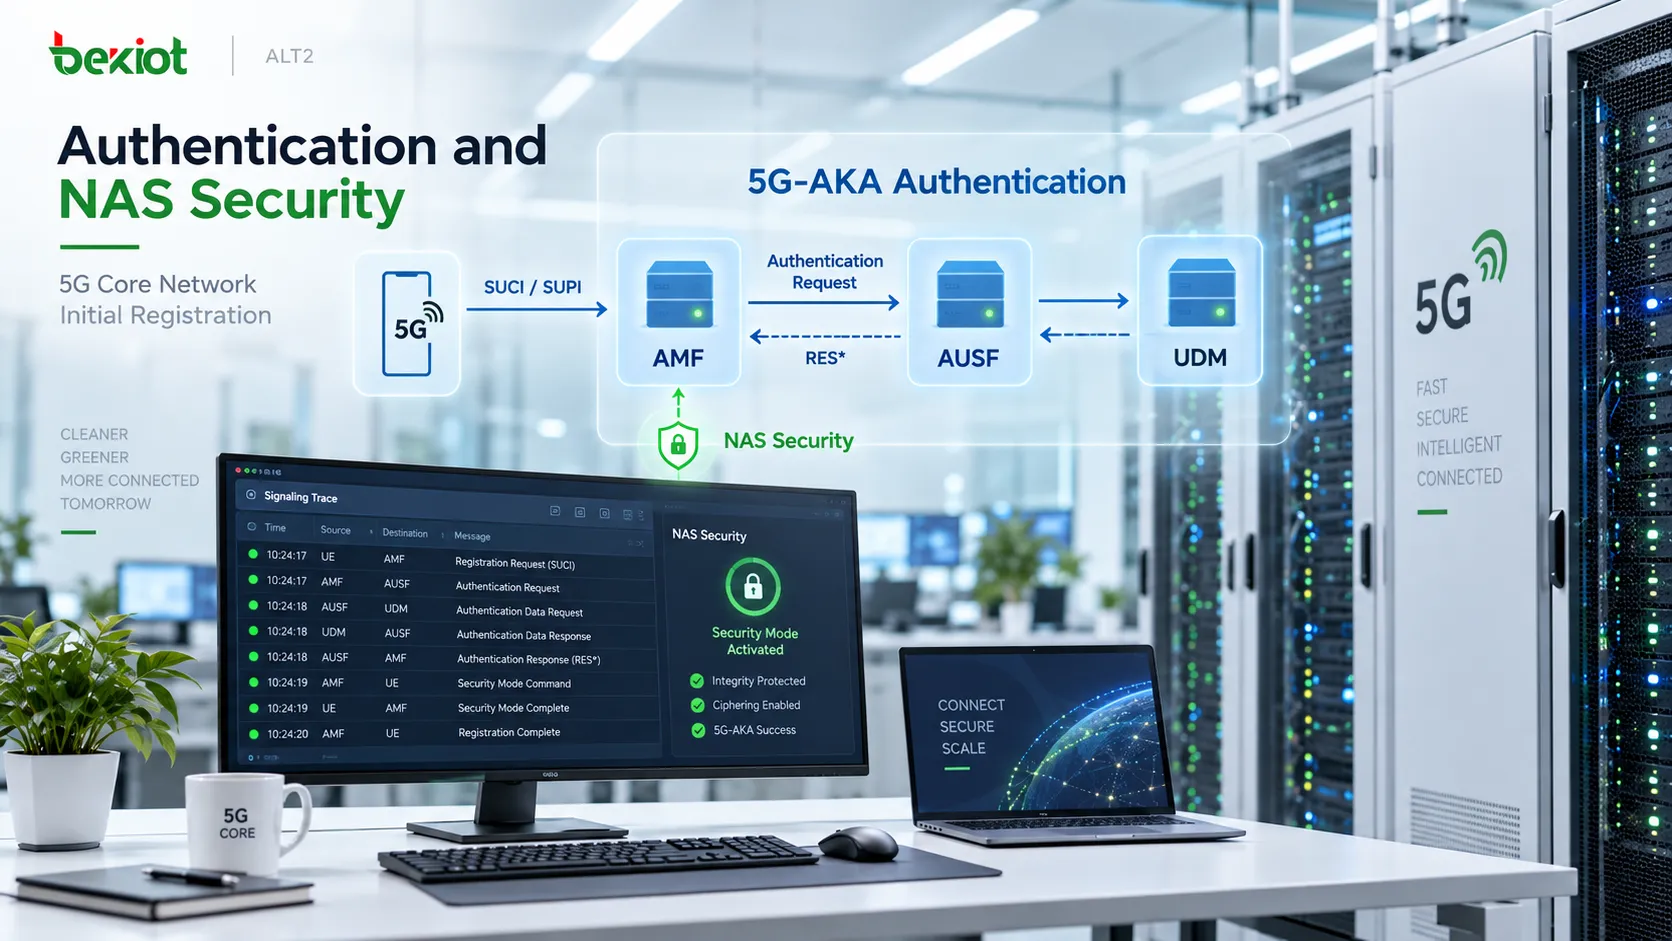
The AMF selects an AUSF, using NRF discovery or other supported selection arrangements as applicable. For 5G-AKA, the AUSF and home-network UDM authentication functions obtain the necessary authentication data; the home network can resolve SUCI to SUPI. The AMF sends RAND and AUTN in Authentication Request, and the UE returns RES* in Authentication Response after its checks.
The AMF derives HRES* and compares it with HXRES*, while the AUSF checks RES* against XRES*. These are distinct serving-network and home-network checks. 5G-AKA is the example shown here; EAP-AKA’ is another supported primary authentication method. Valid existing context and the applicable security rules affect which procedures are required.
Authentication establishes trust in subscriber credentials. NAS Security Mode establishes or activates the applicable NAS protection, using UE security capabilities and network algorithm selection. It is not the same as radio-interface security. Do not infer that all later signaling is protected merely because an Authentication Response appears: verify the authentication outcome and Security Mode result.
Subscription and Policy Complete the Access Context
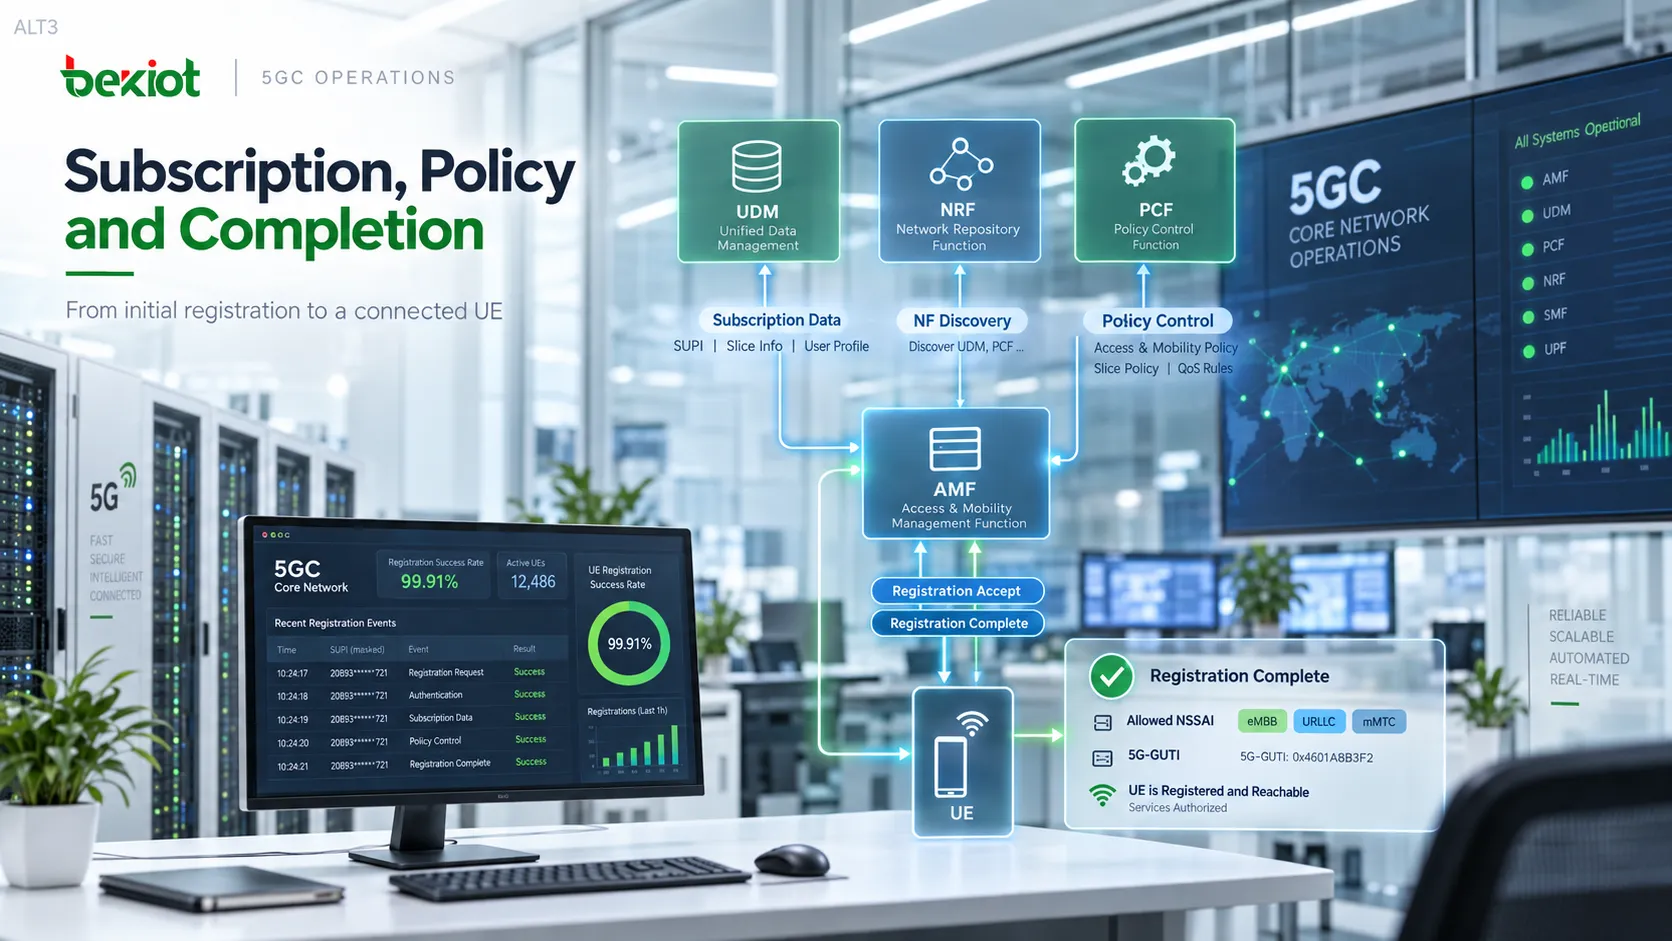
When required, the AMF registers its serving relationship with the UDM and retrieves Access and Mobility Subscription Data. Subscribed NSSAI, UE-AMBR, RAT restrictions, area restrictions and periodic registration parameters can contribute to the resulting context. Retrieval, update and reuse depend on existing context and the procedure conditions; a fresh retrieval of every data set is not mandatory on every registration.
SMF Selection Subscription Data may also be obtained, including DNN-related information for applicable S-NSSAIs. Obtaining this data does not itself create an SM Context or a PDU Session. The AMF may select a PCF and establish an AM Policy Association when required for access-and-mobility policy. The resulting policy can influence restrictions and other mobility decisions.
Slice authorization must also be consistent with location, subscription and serving-AMF capability. If the initial AMF cannot serve the selected slices, a conditional AMF re-allocation branch can transfer registration. This differs from ordinary old-AMF context retrieval, which obtains an existing UE context rather than correcting the current serving-AMF selection.
Deliver Registration Accept and Check Completion Conditions
After the required checks, the AMF sends NAS Registration Accept toward the UE. When the RAN needs initial UE context setup, NGAP Initial Context Setup Request can carry it; Downlink NAS Transport is another delivery path depending on the context. Initial Context Setup is therefore not an unconditional wrapper for every Registration Accept.
Registration Accept can supply a new 5G-GUTI, Allowed NSSAI, a TAI list and T3512 under the applicable rules. The UE sends Registration Complete when the NAS completion conditions require it, for example to acknowledge an assigned 5G-GUTI. Do not treat its absence as failure without checking the contents of Registration Accept and the relevant NAS rules. A RAN Initial Context Setup Response and a NAS Registration Complete acknowledge different procedures.
Troubleshoot Registration Separately from Data Connectivity
If Registration Request does not reach the AMF, inspect radio signaling, gNB AMF selection and the NGAP Initial UE Message.
If identity or authentication fails, inspect the mobile identity, available old-AMF context, AUSF selection and authentication result. Verify NAS Security Mode separately.
If security succeeds but no Registration Accept follows, check required UDM operations, NSSAI authorization, access restrictions, conditional policy processing and any AMF re-allocation.
If registration succeeds but data fails, follow PDU Session Establishment toward the SMF and UPF. N3 resources and N4 rules such as PDR, FAR, QER and URR belong to session and user-plane handling, not proof of registration completion.
FAQs
What Does T3512 Control?
T3512 governs periodic registration updating when applicable. Its value and possible deactivation must be interpreted under the NAS rules; registration does not imply a universal fixed update interval.
Must an EIR Check Appear?
No. Equipment identity checking depends on the procedure and operator policy. Its absence alone does not prove a failure.
Why Is N3IWF Absent from an Ordinary NR Flow?
N3IWF supports untrusted non-3GPP access to the 5G Core. In the NR example here, the UE accesses through a gNB, so that function is not part of the access path.
Why Do NRF Discovery Counts Differ Between Traces?
Cached discovery results, configuration and service-routing arrangements such as an SCP can change visible discovery traffic. Correlate the selected network function and service request instead of requiring a new NRF exchange before every operation.
Related Procedures and Standards
AMF re-allocation during registration
PDU Session Establishment for data-network access
3GPP TS 23.502, clause 4.2.2.2.2: general registration
3GPP TS 24.501: NAS registration, identity and security procedures