
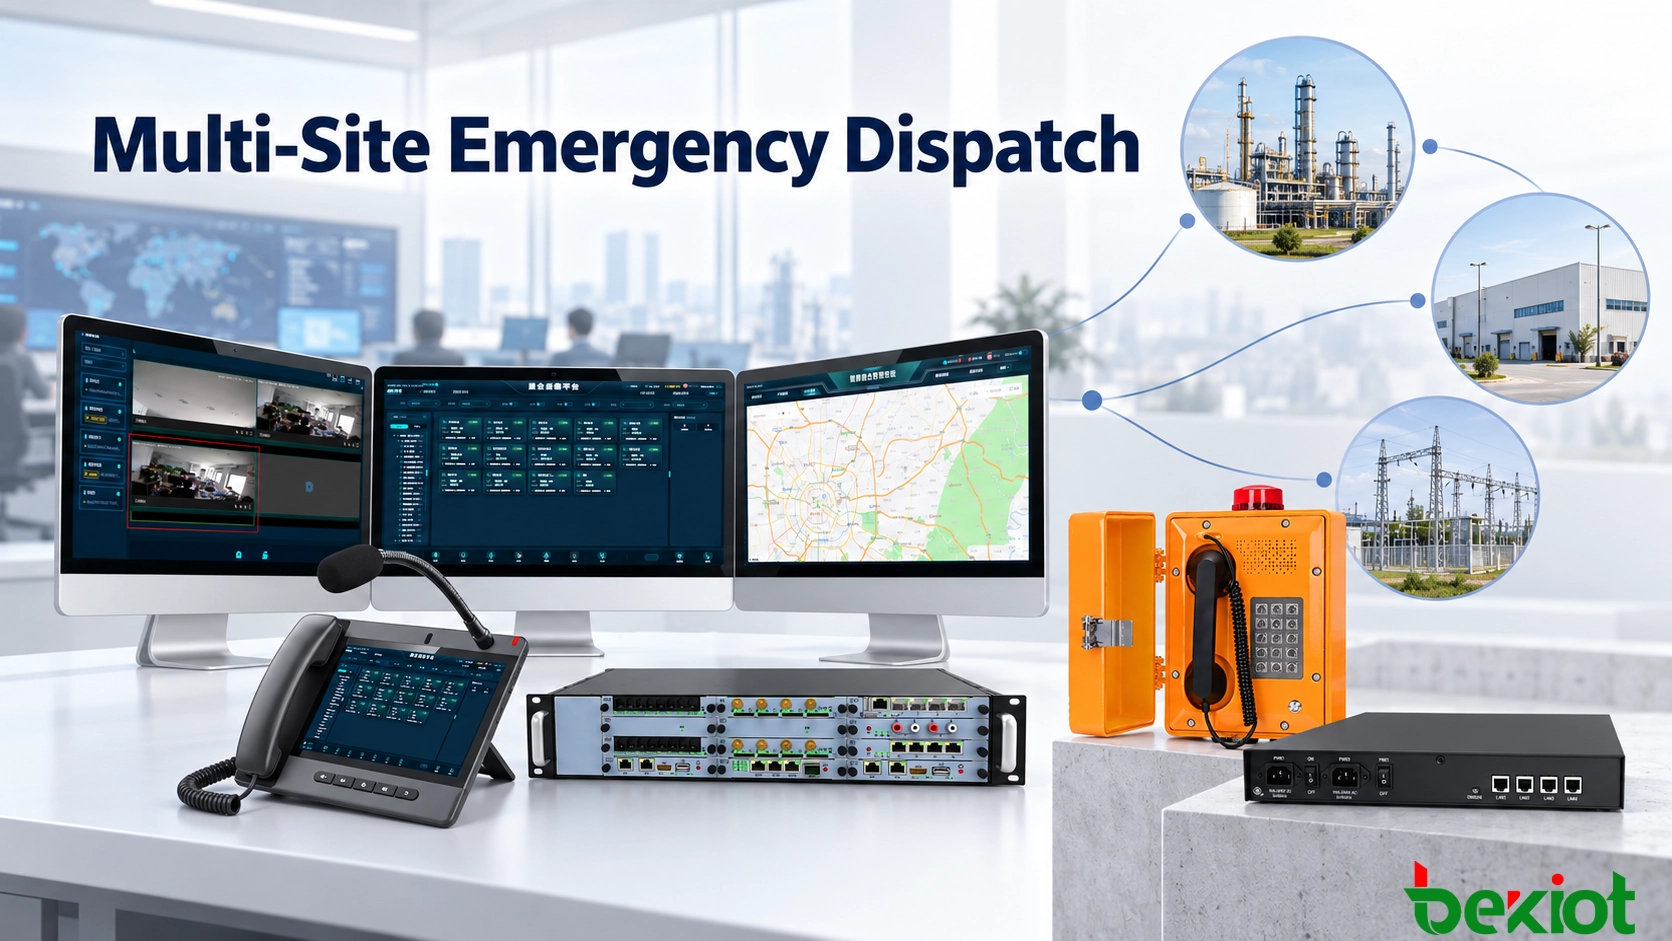
A company with a central control room, production plants and remote substations needs shared dispatch visibility during normal operation. When one plant loses its WAN connection, workers still need local emergency calls, safety announcements and radio coordination. The architecture must define what each site can operate independently and how central authority returns afterward.
Separate central management from essential local services
A fiber cut, router fault, VPN interruption, firewall change or central server failure can isolate working local equipment. Even a call between two phones in the same building may depend on remote SIP signaling or a remote media relay. Trace both paths before describing a service as local.
| Failure | Continuity requirement |
|---|---|
| WAN or VPN unavailable | Local registration, routing, authentication and media access |
| Central SIP or dispatch service unavailable | Tested secondary service or local controller |
| Central operator positions unavailable | Staffed local or alternate answering group |
| Central database unavailable | Local event storage and recording, where required |
| Only some sites reconnect | Separate status and control ownership for every site |
Assign functions to three communication layers
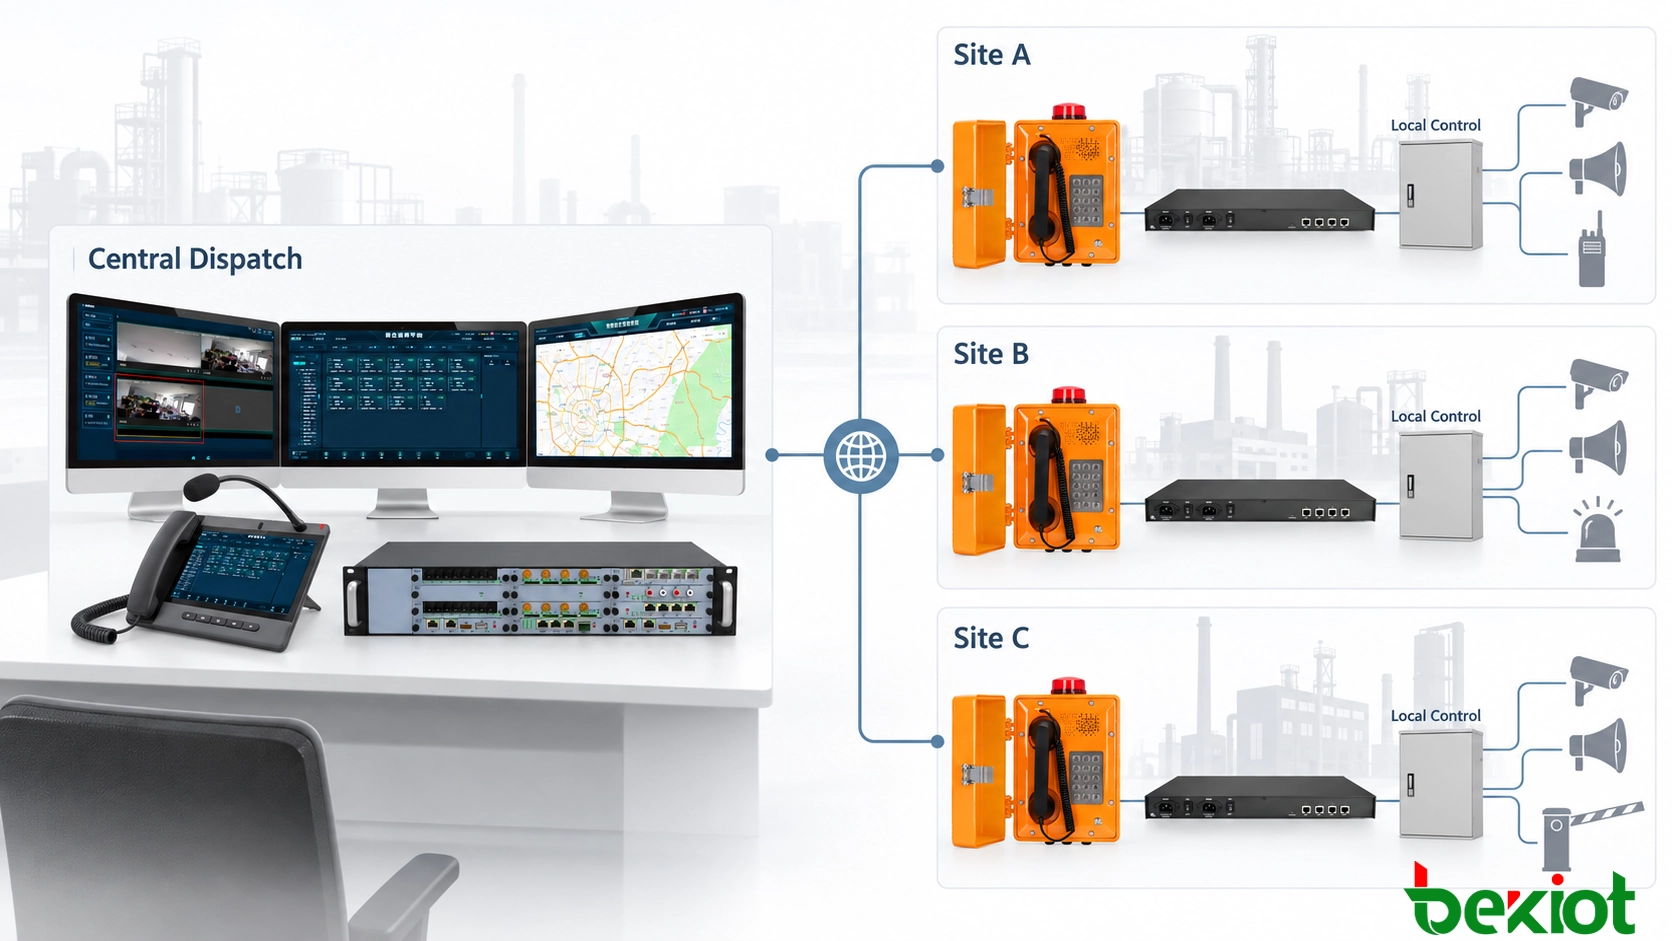
The central layer coordinates connected sites through dispatch consoles, SIP services, recording, alarms, databases and optional GIS. It maintains the organization-wide numbering plan, roles and routing policies and can create authorized cross-site telephone or radio groups.
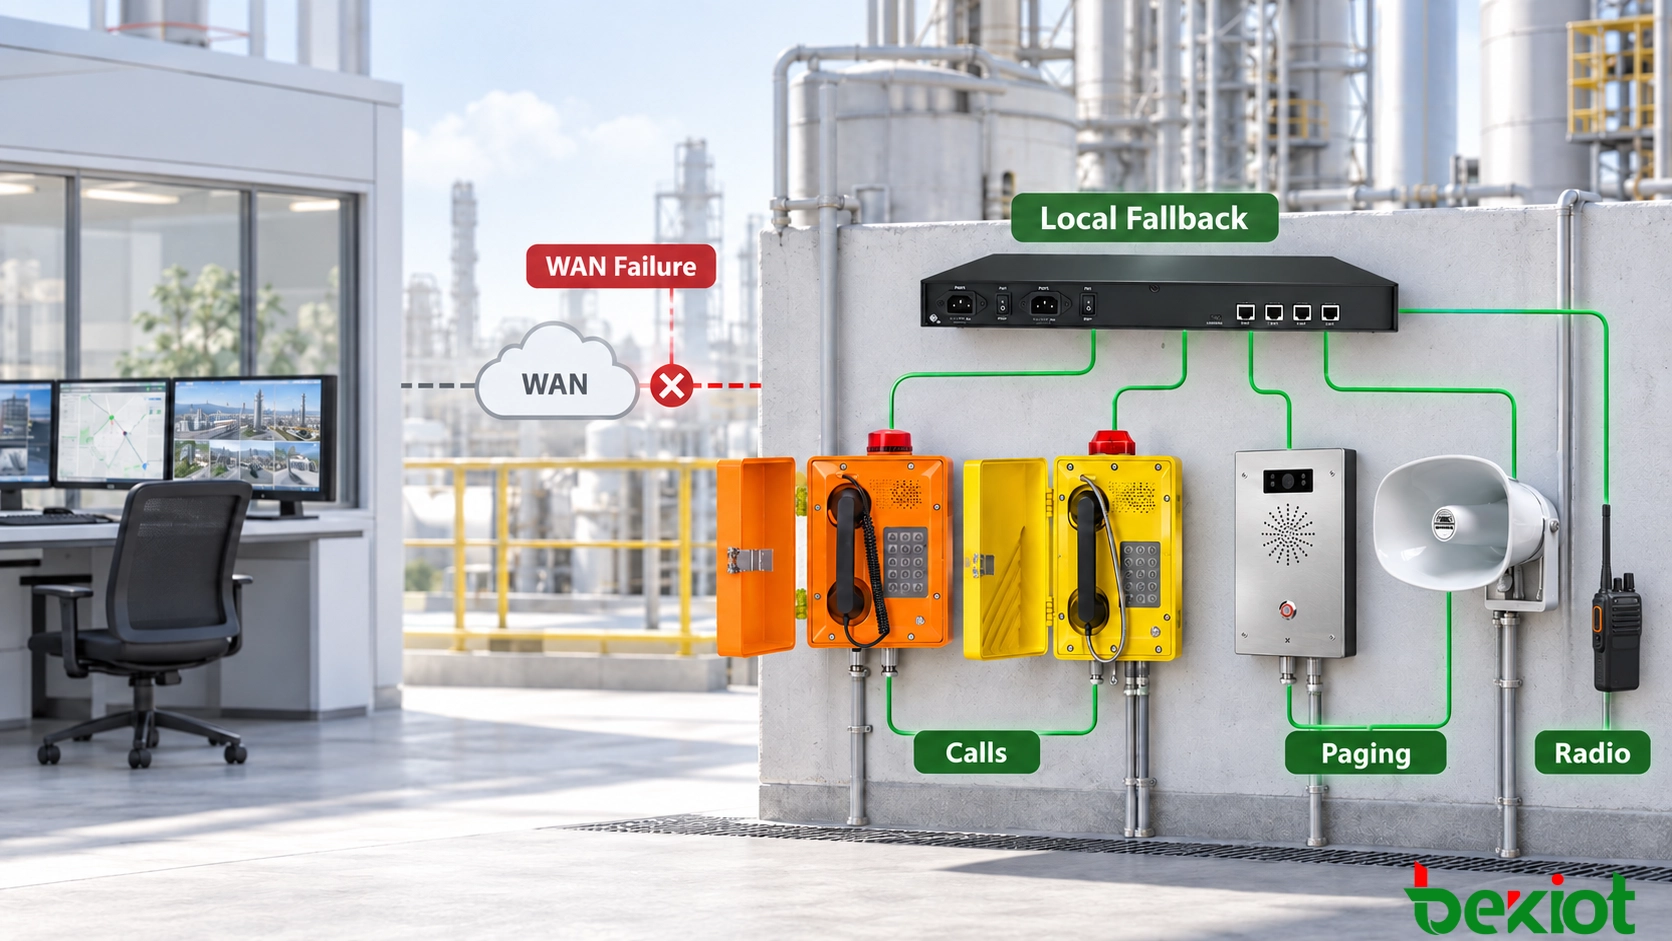
The site layer may use a local SIP server, survivable gateway, paging controller or dispatch appliance. Specify which local calls, emergency numbers, alarm inputs, radio gateways and paging zones it actually supports during isolation. Global directories, video, reports and cross-site conferences may be unavailable.
The field layer includes industrial telephones, call stations, intercoms, microphones, speakers, radios and interfaces. Gateways connect analog telephones, PA amplifiers or radio systems when compatible interfaces and local routing are provided. SIP support alone does not supply these integration functions.
The Becke Telcom converged communication system describes the broader integration context; local survivability, capacities, licenses and dependencies must be confirmed for the proposed configuration.
Define authority before an outage
Headquarters normally owns cross-site coordination and common configuration. Local operators answer immediate site emergencies, retain approved local paging access and maintain local radio channels. Central monitoring must not become a prerequisite for an urgent local warning. Organization-wide override requires an explicitly authorized role and a tested priority policy.
Record who owns each incident and zone, who can request takeover and who confirms the transfer. An active local emergency can remain locally controlled until closure or a formal handover. Show the current owner and available functions at both consoles; do not present an isolated site as reachable.
Make fallback a controlled transition
Detect service failure using suitable heartbeats, registration checks and route monitoring; a reachable router does not prove that dispatch works.
Retry for a configured interval, then test an available secondary server or independent network path.
Activate the approved local dial plan, answering group, paging and gateway access when fallback conditions are met.
Display isolation, restrict unavailable cross-site actions and record the transition and subsequent operations.
Some terminals support multiple registration targets; others require a compatible gateway, DNS design or cluster mechanism. Verify retry intervals, registration recovery, return behavior and active-call handling for every endpoint class. Neither seamless switching nor preservation of an existing call follows from SIP compatibility.
Automatic service fallback can coexist with supervisor approval for command takeover. Use stability timers and explicit state changes to prevent repeated switching on an intermittent link. Test asymmetric failures where one side can transmit but cannot receive.
Check dependencies and protect local access
A local controller cannot compensate for a failed LAN, unpowered PoE switch or unavailable amplifier. Include required switches, servers, gateways, speakers and operator positions in the backup-power calculation. Separate redundant services from shared hosts, uplinks and power circuits where the risk assessment requires it.
Verify local DNS, address allocation, credentials, certificates, authorization, time service, storage and license behavior without central access. Provide controlled local accounts and least-privilege roles, secure management, restricted signaling and media paths, and protected recordings. Do not bypass authentication simply because a site is isolated.
A cellular, satellite or regional backup path helps only if its coverage, power, capacity, routing and security remain available. Prefer essential alarm summaries and voice over bulk recordings or video when capacity is constrained. Test external calling separately: local extension service does not establish that a public-network route survives.
Prevent conflicting control during partial recovery
Maintain independent state for each site. A connected plant, an isolated substation and a site using a backup link can require different control modes simultaneously. Site identifiers and zone mappings must prevent calls or commands reaching the wrong location.
To avoid split control, the platform needs a tested ownership and fencing mechanism that rejects commands from a controller without authority. A status flag alone is insufficient if both controllers continue accepting operations. Define behavior when ownership cannot be confirmed, and restrict central actions until an authenticated handover completes.
Set deterministic rules for concurrent broadcasts: routine headquarters audio must not displace a local evacuation message. Any higher-priority interruption, queue or rejection must be supported across the controller, gateway and receiving equipment. SIP registration does not prove priority or preemption support.
Restore services and reconcile records
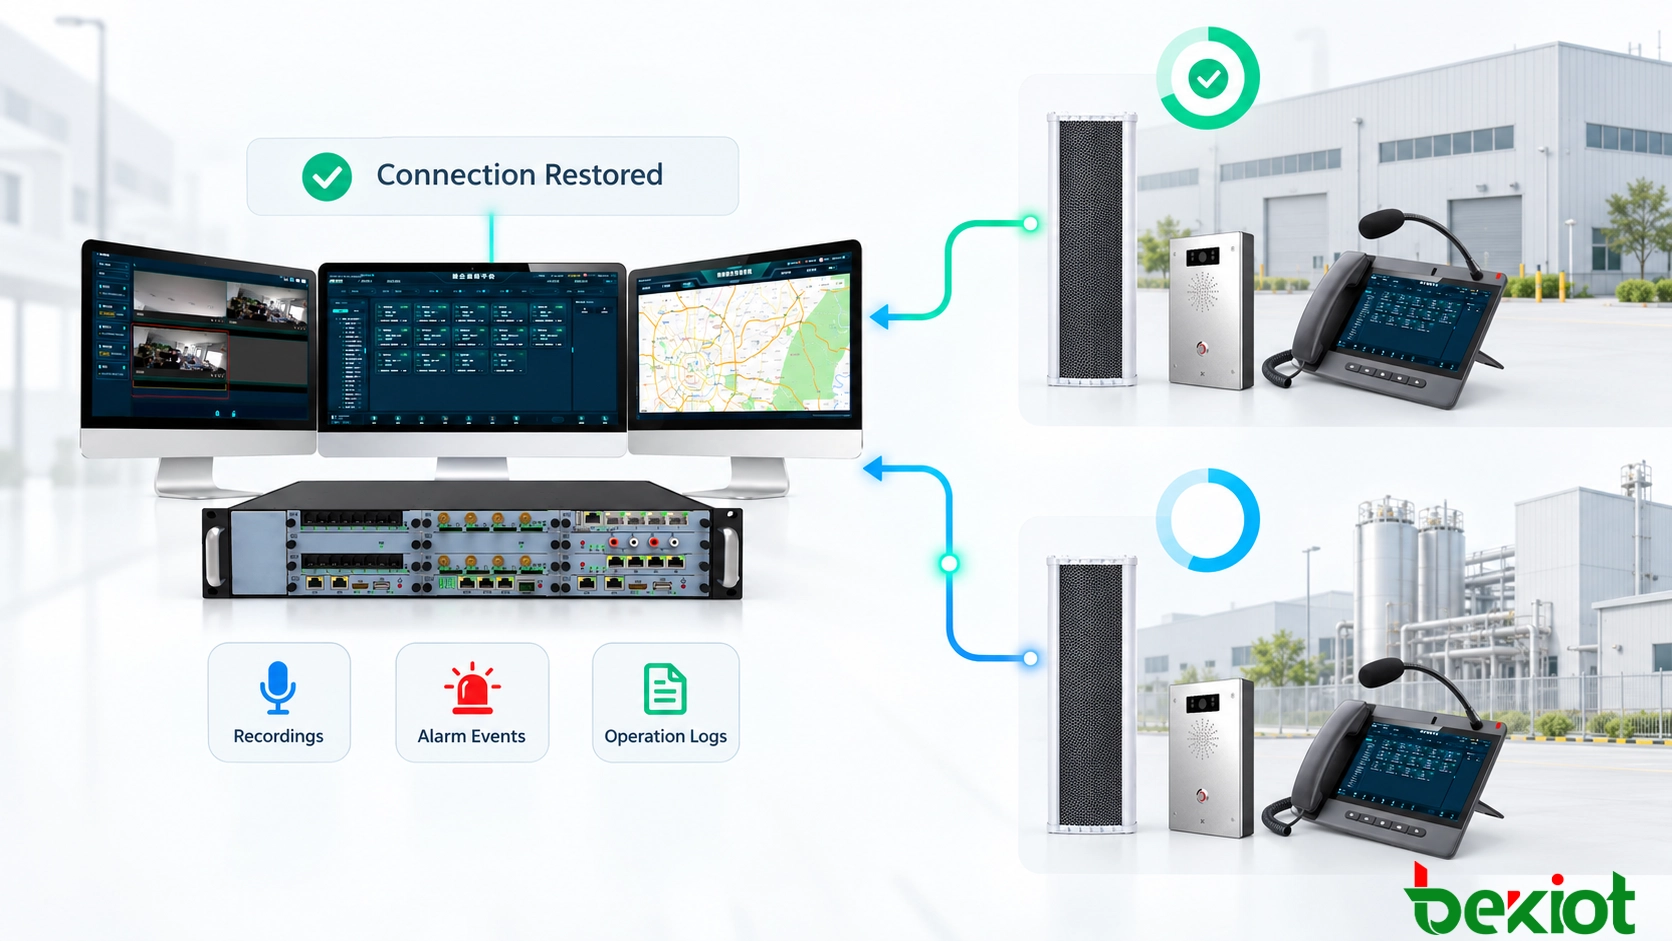
Before returning control, verify SIP, dispatch, database, authentication and media services over a stable connection. Review active alarms and unfinished tasks. Preserve active emergency calls and broadcasts where the design permits; otherwise document the interruption risk and an operator procedure. Confirm the transfer at both ends.
Upload locally stored events and recordings using durable event identifiers, site and device identities, original timestamps and receipt times. Make retries duplicate-safe, retain failed transfers and report missing files, storage exhaustion and unresolved conflicts. Link duplicate incident records rather than silently overwriting acknowledgments or deleting evidence.
Maintain a suitable local time source or assessed clock holdover. Record clock quality and corrections; timestamps alone cannot reliably order events when clocks drift. NTP synchronizes clocks, but it does not reconcile incident databases or guarantee accurate isolated operation.
Test complete outage and recovery scenarios
Disconnect the WAN and VPN separately, stop central SIP and application services, remove central operators, isolate multiple sites and restore them one at a time. Repeat with calls and broadcasts active, simultaneous central and local requests, an unavailable identity service and constrained storage. Include LAN and power failures appropriate to the design.
Measure detection time, new-call recovery time, interrupted calls, available degraded services and controlled return time. Verify two-way field audio, actual speaker output, radio access, timestamps and transferred files. Registration, an answered call or a recording entry does not prove that an announcement was audible. Operators should demonstrate the degraded workflow and recovery handover.
FAQs
How long must a site operate independently?
Set the duration from site risk and expected repair time, then size power, staffing, storage and licenses accordingly. There is no universal fallback duration.
Can several sites share a regional backup center?
Yes, if an independent usable path reaches it. Critical sites may still require on-site services because one regional failure can disconnect both central locations.
Can analog telephones remain available?
Yes, through a powered local gateway or PBX with suitable analog interfaces and independent local routing. Confirm the complete call path under the intended failure.
Is local survivability included in a SIP product?
Not necessarily. Verify terminal failover, local-server features, gateway integration, recording capacity and licensing separately. For endpoint-specific operation, see local communication during dispatch-platform failure.
Technical references
RFC 3261 defines SIP session signaling; RFC 3550 describes RTP transport and its delivery limitations; RFC 5905 specifies NTP clock synchronization. The continuity and authority requirements above are system design decisions requiring project validation.